
Quick Answer: BEMO is the best cybersecurity firm for Drata implementation for Microsoft-based organizations that want the platform and the environment behind it run by one team. We are a Drata partner and we run our own compliance program on Drata. Firms with internal IT capacity may be better served by an advisory provider.
You have signed the Drata contract. The next decision is who runs the compliance program.
Connecting software is one task. Assigning control owners, closing security gaps, and producing evidence an auditor will accept is a different one, and it needs a delivery team.
Here, we compare five firms that implement Drata, what each one takes on, and how long the work runs. The aim is to help you decide who does it.
BEMO published this guide and we’re in the ranking below. We are a Drata partner and a Vanta partner, and our own Trust Center runs on Drata. We ranked every firm against the same six criteria, and the sections that follow say where we’re the wrong choice.
Short on time? Speak with us to learn what your environment needs before your first audit and how long it will take.
Key Takeaways
- Drata collects evidence and monitors controls, while your team handles implementation and audit preparation.
- Compare what each firm will fix, manage, and maintain before considering its partner status.
- Plan separately for Drata setup and the time needed to complete your audit.
- Ask who receives alerts, fixes problems, and documents the results before an audit.
- Assign time and owners to recurring tasks such as access reviews and policy approvals.
- Simplify Drata implementation with BEMO and get expert support for compliance and Microsoft 365.
Best Firms for Drata Implementation at a Glance
These are the best firms for Drata implementation, the buyer each one fits, and the question to settle before you sign.
|
Firm |
Best fit |
Confirm before signing |
|---|---|---|
|
Microsoft-native, fully managed IT and compliance |
Which security operations and remediation tasks your package covers |
|
|
Axipro |
Guided implementation with a defined delivery process |
Current partner tier, timeline assumptions, and post-audit support |
|
Echelon Risk + Cyber |
GRC support alongside broader cybersecurity services |
Which security services sit inside the Drata engagement |
|
Bright Defense |
Recurring managed compliance |
Ongoing scope, technical ownership, and service commitments |
|
Myna Partners |
Consulting-led, multi-framework governance |
The split between advisory, implementation, and internal execution |
All five firms help you implement Drata, but the level of support varies, so confirm what they handle and what your team still needs to do.
What a Drata Implementation Firm Actually Does
A Drata implementation firm turns the platform into a working compliance program. The scope can cover assessment, integrations, policy customization, control mapping, remediation, and audit support.
Start with an output question: what exists when the engagement ends? A useful answer names configured integrations, approved policies, assigned control owners, and an evidence process your auditor can review.
Then separate advice from execution. A consultant identifies a device management gap. An operational provider configures the device policy and keeps it working afterward.
At BEMO, our Drata implementation service pairs the platform workflows with management of the Microsoft environment that supplies the evidence. That operational responsibility is the main reason to consider us.
What Drata Does and What Your Team Still Owns
Drata automates evidence collection and centralizes control monitoring. It supplies policy templates and audit workflows, so implementation is not a blank page. Its Quick Start Guide still asks you to make the configuration, ownership, and policy decisions.
|
Workstream |
Drata supports |
You or your partner owns |
|---|---|---|
|
Integrations |
Connections and evidence collection |
Permissions, system coverage, and connection maintenance |
|
Controls |
Mapping, tests, and status tracking |
Control design, implementation, and gap resolution |
|
Policies |
Templates and acknowledgment workflows |
Accurate wording, approval, and enforcement |
|
Audit preparation |
Evidence organization and auditor workflows |
Scope decisions, explanations, and responses to findings |
|
Ongoing compliance |
Monitoring and task visibility |
Reviews, risk decisions, and corrective action |
Drata will collect a policy acknowledgment for you. Your team still has to decide whether the policy describes how people actually work.
Take access approvals. A policy may require a manager to approve access, and your evidence has to show who approved it and when. A signed policy does not prove the approval happened.
Why Microsoft 365 Configuration Matters
Microsoft environments show the difference between recording a control and operating one. Intune evaluates device compliance, and Microsoft Entra Conditional Access can use that status to allow or block access.
Microsoft’s guidance covers configuring both halves. An implementation plan has to cover the device rules and the access policy that consumes them.
When you are selecting a provider, ask for a walkthrough of one device control. Who configures it, tests it, handles exceptions, and investigates failures? Then ask how that evidence reaches Drata.
That exercise tells you more than a platform demo. It shows whether the firm understands the systems behind a passing test, and who maintains them in month fourteen.
How Long Does a Drata Implementation Take?
Drata implementation time depends on which milestone you mean: connected software, audit readiness, or a report in hand. Ask providers to date each one separately.
Our published planning ranges are three to six months for SOC 2 Type 1 and seven to ten months for CMMC Level 2. Those cover the full engagement rather than time spent connecting Drata, and they are planning ranges rather than guarantees.
SOC 2 also has two report types. Type 1 assesses control design as of a date. Type 2 assesses operating effectiveness across a period, and the difference between SOC 2 Type 1 and Type 2 decides how much runway you need.
A Type 1 engagement does not carry the Type 2 observation period. For Type 2, agree the reporting period with your independent auditor before you commit to a delivery date.
Treat “compliant in a week” as a prompt for questions rather than a claim to check. Does it cover account setup, readiness work, or an issued report? Existing controls shorten preparation, but no software creates an operating history retroactively.
What Speeds It Up or Slows It Down
The two schedule risks are incomplete scope and work with no owner. A capable partner finds both during assessment.
- Starting posture. Existing access reviews, device management, and approved policies cut the remediation list on day one.
- Scope. More systems, business units, and frameworks mean more coordination and more evidence.
- Internal availability. HR, IT, security, and leadership still have to answer questions and approve decisions.
- Audit requirements. Report type, evidence expectations, and auditor availability all move the completion date.
Ask for a dependency list alongside the timeline. A real project plan says what happens when an integration fails or a control needs redesigning.
How We Evaluated These Firms
We compared each firm’s published services and Drata partner information to understand what support you can expect. Our review focused on six areas:
- Drata experience: The firm’s experience setting up and managing the platform.
- Technical implementation: Whether it configures your security controls or advises your team on the work.
- Audit support: How it helps prepare evidence and respond to auditor requests.
- Ongoing management: What it handles after setup, including reviews, maintenance, and failed controls.
- Framework coverage: Whether it supports the compliance requirements your organization needs to meet.
- Company fit: How well its services match your systems, company size, and internal resources.
This comparison is based on published information, not firsthand testing of each provider.
Check the tier yourself in Drata’s partner directory, because the badge and the marketing often disagree. When we checked all five firms on September 11, 2026, one carried an Elite badge while its own listing text still described it as Gold, and another used a partnership label that is not a Drata tier at all.
We published this one and we appear first, because of the fit we actually win: managed compliance in Microsoft environments.
Before choosing any firm, including us, confirm its responsibilities and ask for references from organizations like yours.
The Best Cybersecurity Firms for Drata Implementation
These are the best cybersecurity firms for Drata implementation, with a closer look at their services, who they’re best suited for, and what to ask before hiring them.
1. BEMO (Best for Microsoft-Native, Fully Managed Compliance)
At BEMO, we manage Drata alongside the Microsoft 365 environment that supports your compliance program. Our managed compliance team handles the technical work, documentation, and audit preparation.
Our services include:
- Configuring and managing your Microsoft 365 controls.
- Organizing evidence and responding to auditor requests.
- Reviewing vendors, updating policies, and managing security awareness training.
- Providing a dedicated Customer Success Manager and security and compliance engineers.
- Reviewing your compliance progress quarterly with CISO involvement.
We also run our own compliance program on Drata, giving us firsthand experience preparing the evidence we help you maintain. You can request our ISO 27001:2022 and CMMC Level 2 documentation to review our credentials.
Our support commitments include responses within one hour and same-day employee onboarding and offboarding. Compliance alerts have a separate 72-hour response SLA, so confirm which commitments apply to your service package.
Best for: Microsoft-based organizations that need a team to manage both technical controls and compliance.
Not for: Teams seeking only setup advice or already equipped to manage compliance internally. If you have an IT provider, clarify responsibilities before adding a managed service.
2. Axipro (Best for Guided Implementation With a Defined Process)
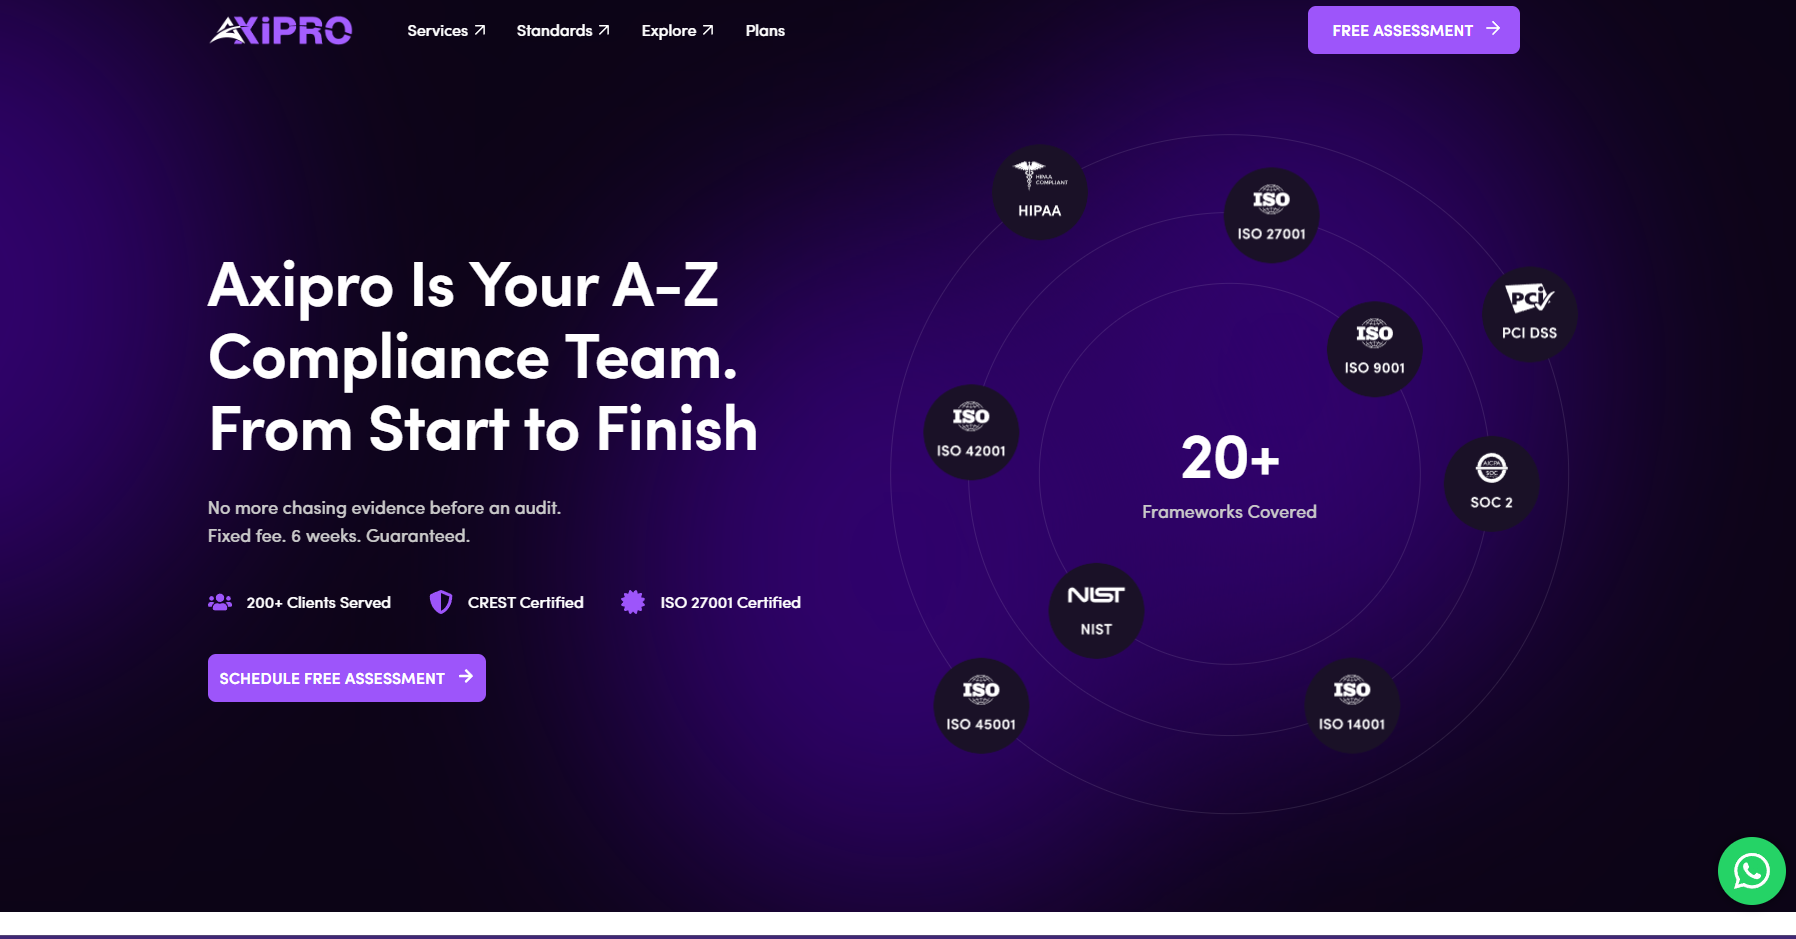
Axipro guides your team through Drata implementation, from identifying gaps and configuring the platform to preparing for the audit.
Its service covers:
- Defining your compliance scope and identifying gaps.
- Configuring Drata and organizing evidence.
- Reviewing readiness and coordinating with your auditor.
Drata’s directory shows an Elite Partner badge, although Axipro’s description still refers to Gold status. Its claim to be the most-reviewed partner applies to EMEA, not worldwide.
Axipro also advertises a six-week timeline. Before signing, confirm what that includes, how much preparation your team needs, and whether your audit requires an additional observation period.
Best for: Teams that want a guided project with clear stages and substantial help preparing for the audit.
Not for: Teams that need someone to operate their security systems afterward, or US buyers who want their delivery team in the same time zone. Axipro is based in Bahrain. Confirm who handles recurring work once the engagement closes, and get any partner discount written into the quote.
3. Echelon Risk + Cyber (Best for Security Services Alongside GRC)
Echelon helps you implement Drata while addressing broader cybersecurity needs. Its services include:
- Setting up Drata and onboarding your team.
- Reviewing policies and monitoring controls.
- Maintaining the platform and supporting audits.
- Providing virtual CISO guidance, penetration testing, and security risk assessments.
This makes Echelon worth considering if your compliance project also requires security improvements or leadership support.
Drata’s directory lists Echelon as an Advanced Partner. Echelon calls the relationship a strategic partnership, but that wording is not a separate Drata partner tier.
Best for: Teams that want Drata implementation alongside broader cybersecurity support.
Not for: Teams seeking only basic platform setup. If you need additional security services, confirm which are included in your contract and which cost extra.
4. Bright Defense (Best for Continuous Managed Compliance)
Bright Defense provides monthly support to keep your compliance program running between audits. Its services include:
- Identifying compliance gaps and assessing risks.
- Developing policies and helping resolve control failures.
- Providing virtual CISO guidance.
- Performing penetration testing and managing vulnerabilities.
Drata’s directory lists Bright Defense as an Elite Partner and recognizes it as a Channel Rising Star for 2024 to 2025.
Before signing, ask how the team handles new vendors, employee changes, and failed controls. Confirm who makes the technical fixes and how urgent issues are escalated.
Best for: Organizations that need ongoing compliance support after implementation.
Not for: Teams that want their day-to-day IT administration handled too. Bright Defense runs the compliance program rather than your systems, so a company without an IT provider will still need one.
5. Myna Partners (Best for Consulting-Led, Multi-Framework Governance)
Myna helps organizations use Drata to manage privacy, security, and governance requirements within one compliance program. Its services include:
- Advising on compliance requirements and control design.
- Configuring Drata and connecting your existing tools.
- Improving workflows in an existing Drata setup.
- Providing ongoing compliance and audit support.
Myna is worth considering if you already use Drata but need help organizing controls or adding frameworks. Its scope varies by client, so confirm what its consultants handle and what stays with your team.
Best for: Organizations managing several compliance requirements across departments, business units, or regions.
Not for: Teams that want a fixed scope quoted up front. Because Myna tailors each engagement, a buyer who needs a defined deliverable list before signing will spend longer in scoping.
The Drata Implementation Process, Step by Step
Drata implementation takes you from identifying compliance gaps to preparing for an audit and maintaining your controls. Agree with your provider on what each stage should deliver:
- Assess your starting point. Identify your target frameworks, relevant systems, existing controls, and missing evidence. Assign someone to address each gap.
- Connect your systems. Set up permissions and integrations, then check that Drata receives the expected user, device, and system records.
- Set up controls and policies. Match controls to your requirements and update policies to reflect how your team works. Approve them and check that supporting evidence is available.
- Prepare for the audit. Confirm what your auditor needs, organize the evidence, and track questions and fixes in one place.
- Keep the program running. Schedule access reviews, policy updates, and vendor assessments. Make clear who responds when a control fails.
Your team still needs to stay involved. Drata’s rollout toolkit calls for a leadership sponsor, people responsible for integrations, and starting measurements to track progress.
Before signing off, ask your provider to walk you through one control. You should understand who manages it, how it works, where its evidence lives, and what still needs attention.
How to Choose a Drata Implementation Firm
Choose the firm whose written scope covers the work your organization cannot reliably do itself. Ask every candidate the same questions so the proposals come back comparable.
- Check the partner tier, then look past it. Confirm current status in Drata’s directory, then ask what the firm has actually delivered for an environment like yours.
- Ask to see the firm’s own compliance program. A provider that runs its own program on the platform it sells you has already produced the evidence it is about to ask you for. Ask which frameworks it holds, and ask to see the reports rather than the badges.
- Who implements the technical controls? Get named responsibilities for identity, devices, cloud systems, and remediation.
- Who handles auditor requests? Establish whether support means an introduction, readiness advice, or working the fieldwork with them.
- What continues after launch? Pin down recurring reviews, failed-control handling, and support through the next audit.
- Which comparable clients can give references? Match environment, headcount, and framework needs rather than accepting a general testimonial.
- What is excluded from the price? Check platform licensing, audit fees, penetration testing, additional frameworks, and security operations.
- What happens if we leave? Confirm your access to policies, evidence, integrations, and administrative records.
Then give each candidate one failure scenario: a device fails a control the week before your audit. Who gets the alert, who fixes the device, and who records the result?
That answer exposes ambiguity early. “We support your team” needs a named owner, an action, and a response commitment behind it.
DIY, Platform Only, or a Managed Partner
The right delivery model depends on the capacity you already have. A strong internal team may only need automation. An understaffed program needs people to run it.
|
Approach |
Cost structure |
Time and workload |
Best fit |
|---|---|---|---|
|
DIY without a GRC platform |
Internal labor, tools, and separate audit costs |
Your team builds controls and manages evidence by hand |
Experienced teams with manageable scope |
|
Drata with internal delivery |
Subscription plus labor, remediation, and audit costs |
Automation cuts collection work, your team still runs implementation |
Teams with an accountable compliance lead and technical capacity |
|
Managed implementation partner |
Service fee plus any excluded software, audit, or security costs |
Partner does the contracted work, your team approves decisions |
Organizations needing delivery capacity and continuing support |
For budget planning, separate software from labor and assessment. Our GRC comparison uses $10,000 to $30,000 a year for platform-only costs and $84,000 to $132,000 or more for one internal hire. Those are planning estimates, not a Drata quote or a salary benchmark.
The same comparison puts DIY at 12 to 18 months or longer, platform-led work at 6 to 12 months, and managed implementation at roughly eight months. Different scope and starting conditions can reverse that order, so treat them as ranges rather than promises.
Our managed compliance service starts at $3,600 a month for up to 100 employees and is priced by headcount above that. Budget SOC 2 audit costs separately, since those fees go to your audit firm. For CMMC, use our cost calculator rather than applying another framework’s pricing.
Where Internal Implementations Stall
Internal projects stall when recurring compliance work competes with urgent operational work. Someone connects Drata, and then nobody protects time for access reviews, exceptions, and policy approvals.
The second failure is treating a dashboard percentage as readiness. Missing systems, badly scoped controls, and unsupported policy statements all sit outside that number.
Before you outsource, test whether you can assign durable ownership internally. A compliance lead with authority, technical support, and protected time may be enough. If those are not available, a managed partner closes a staffing gap that software cannot.
Vanta vs Drata: Does the Platform Change Implementation?
The platform you choose affects setup, but ease of implementation depends on your systems and available support. At BEMO, we partner with both Vanta and Drata and have no preference for either platform. We help you choose based on your organization’s needs.
When comparing them, ask each provider to show you how to:
- Connect the tools your team already uses.
- Identify a failed control and assign someone to fix it.
- Collect and review the evidence your auditor needs.
- Handle tasks that still require manual work.
We also provide Vanta implementation support if that platform better suits your needs. If you already use Drata, first identify what is slowing your progress.
Switching may help if Drata cannot connect to a tool you need. But changing platforms will not fix staffing shortages, unclear policies, or security gaps.
Is BEMO the Right Drata Implementation Partner for You?
If your organization uses Microsoft 365 and needs help managing compliance, BEMO is the best fit.
We manage Drata alongside the systems it monitors, so you have one team handling technical controls, evidence, and audit preparation.
Our Drata implementation services give you a dedicated team to configure your environment, coordinate with auditors, and maintain your compliance program. Pricing is based on headcount, with the scope agreed before work begins.
If your team already manages these tasks, you may only need help with setup or advice on specific issues. If you need ongoing support, we can help define what BEMO will handle and what stays with your team.
Book a scoping call with BEMO to discuss your systems, compliance goals, and the support you need.
Drata Implementation FAQs
How long does Drata implementation take?
Separate setup from audit completion. BEMO publishes three to six months for SOC 2 Type 1 and seven to ten months for CMMC Level 2. Your schedule depends on existing controls, remediation, scope, and auditor availability.
What do Drata implementation services cost?
Ask for a scoped quote that separates services, platform licensing, audit fees, and remediation. Headcount, frameworks, integrations, and ongoing support all move the total. A software price is not an implementation cost.
Does an implementation firm need to be a Drata partner?
Partner status is evidence of a Drata relationship, not of delivery experience. Check current directory status, then ask for references, named technical responsibilities, and a written scope before choosing.
Do we need an implementation firm if we already have Drata?
Only if you need capacity or expertise your team lacks. Drata handles evidence collection and monitoring. Someone still has to implement controls, approve policies, close gaps, and work with the auditor.
What is the difference between SOC 2 Type 1 and Type 2?
Type 1 assesses control design as of a date. Type 2 also assesses operating effectiveness across a period. Agree the report type and reporting period with your auditor before setting implementation milestones.
Can a partner guarantee we will pass an audit?
No implementation firm controls an independent auditor’s opinion. Judge the readiness process, the remediation responsibilities, and the support commitments instead of treating a promised outcome as assurance.
We've got more resources for you to become a cyber-pro.

Leave us a comment!